
Key Takeaways
Trump addressed the hack before the FBI attributed it to North Korea.North Korean actors converted stolen assets into ether, the bureau said.Binance reported 90% replenishment and targeted a Sunday restart.
Trump Examines North Korea Link and Binance Assurances
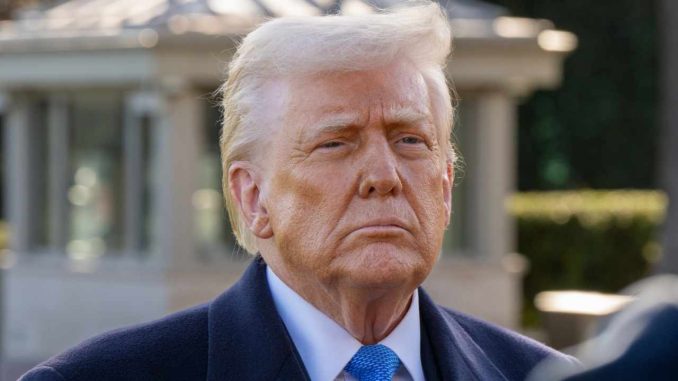
President Donald Trump said on Oct. 30 that U.S. officials were looking into the Binance hack and possible North Korean involvement. He spoke during an Oval Office meeting with Stephen Hubbard, an American recently released from a Russian prison.
When asked about North Korean responsibility regarding the hack of Binance, Trump stated:
“We’re looking at that.”
Addressing prospects for recovering the money, Trump cited Binance’s assurances: “Well, they say they’re gonna get it back, and they’re guaranteeing it or something. They are.”
Comparing digital transactions with signing a check, he added: “I’ve always felt it was a little bit dangerous. But no, they say they have it pretty much under control. We’ll see.”
FBI Attributes Binance Attack to North Korea
The Federal Bureau of Investigation (FBI) attributed the theft to North Korea on Oct. 31, stating:
“The Federal Bureau of Investigation (FBI) is releasing information advising the Democratic People’s Republic of Korea (North Korea) was responsible for the theft of more than $6 billion USD in virtual assets from cryptocurrency exchange Binance, on or about October 29, 2026.”
The FBI, the U.S. Secret Service, and the Internal Revenue Service’s Criminal Investigation division observed the attackers converting stolen assets primarily into ether. The bureau expected further conversions through decentralized finance platforms and instant swap services, which exchange one cryptocurrency for another. It identified the North Korean cyber activity as Tradertraitor.
The FBI urged cryptocurrency exchanges, blockchain infrastructure operators, analytics firms, and other digital asset service providers to block transactions involving or originating from addresses used by the attackers. The alert listed addresses associated with laundering the stolen assets and called for private-sector assistance in disrupting those transfers.
Chainalysis and TRM Labs had also attributed the attack to Tradertraitor, a North Korean cybercrime group targeting cryptocurrency platforms and investors. Chainalysis’s North Korea findings included stolen Binance assets mixing with proceeds from September’s Bitget theft, previously attributed to North Korean actors. Separately, TRM Labs expressed high confidence in its assessment, citing onchain and offchain intelligence.
Investigators traced thousands of transfers through public blockchain transaction records, including repeated returns to previously used wallets. Chainalysis said the pattern suggested automated laundering, with software repeatedly moving funds to obscure their origins.
Replacement Purchases Narrow Binance’s Shortfall
Binance’s recovery plan reserved more than $6.34 billion in company funds, excluding approximately $3 billion in frozen assets. Matching token holdings initially covered about 80% of losses.
An Oct. 31 update put replenishment at 90% with 10 cryptocurrencies, including BTC, ETH, and XRP, fully backed. Replenishment drew on company funds, its emergency Secure Asset Fund for Users, and futures insurance reserves. Binance was sourcing less liquid tokens to cover the remaining shortfall and pledged to absorb all losses. These purchases replaced affected assets separately from recovering stolen funds.
Withdrawals remained targeted for Sunday, Nov. 1. Binance published a reserve snapshot taken at midnight Coordinated Universal Time (UTC), the international time standard, on Oct. 31. The full cryptographic proof was expected by Nov. 3, allowing holders of the 10 listed tokens to verify minimum 1:1 backing.



Be the first to comment